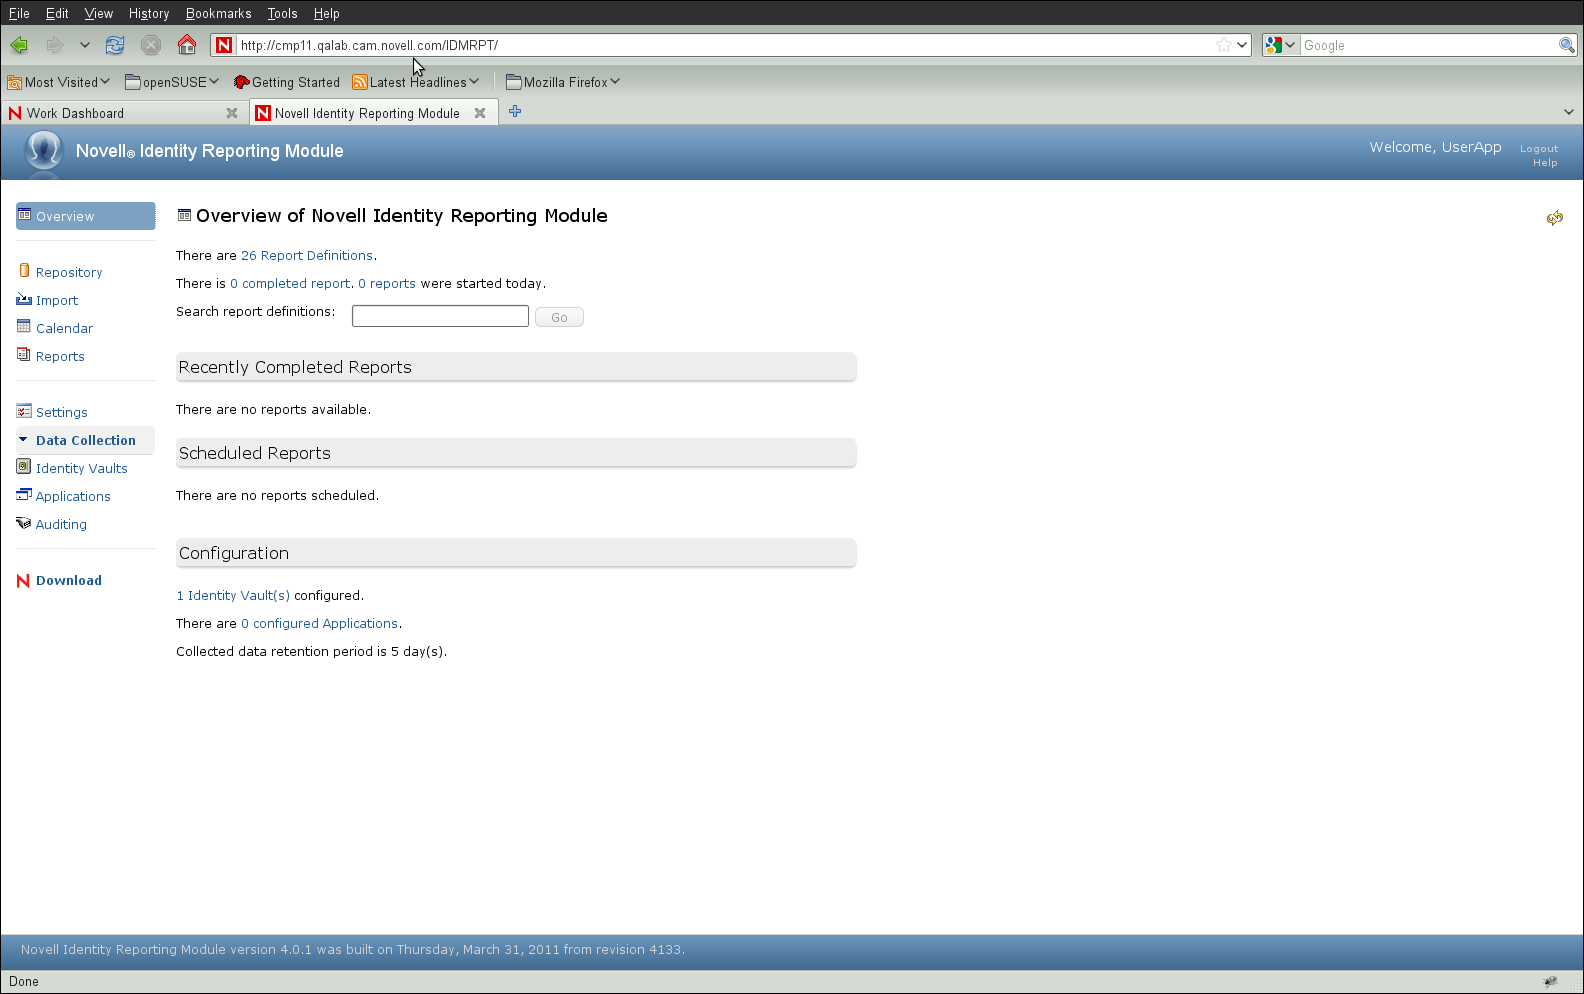
3.1 Accessing the Identity Reporting Module
You can access the Identity Reporting Module directly from a browser, or launch it from the Roles Based Provisioning Module.
NOTE:To access the reporting module, an LDAP user must be a Reporting Administrator and also be able to read all of the attributes in his/her own user object. Therefore, you need to grant the user read trustee rights to the user’s own nrfMemberOf attribute.
3.1.1 Starting the Reporting Module Directly with a URL
To access the Identity Reporting Module directly, open a Web browser and go to the address (URL) for the module (as supplied by your system administrator). The URL will follow this pattern:
http://server:8180/IDMRPT/
3.1.2 Launching the Reporting Module from the User Application
If you want to be able to launch the reporting module from the Work Dashboard in the User Application, you need to have your Configuration Administration specify the URL for the reporting module on the tab. The Configuration Administrator needs to specify the URL in the field within the page. In addition, you need to have the navigation permission. The Report Administrator is given this permission by default.
To access the Identity Reporting Module from the User Application:
-
Log into the User Application as a Report Administrator.
-
Click in the User Profile section of the Work Dashboard:
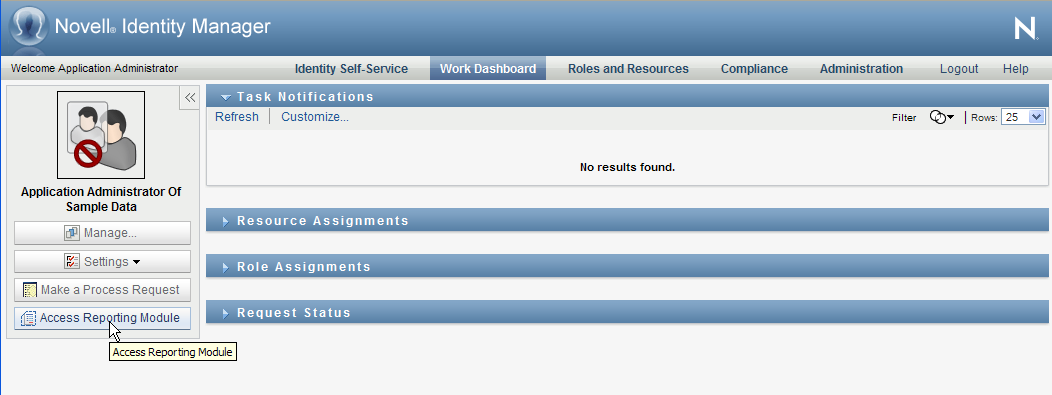
When you click this button, the login window for the reporting module opens in a new window:
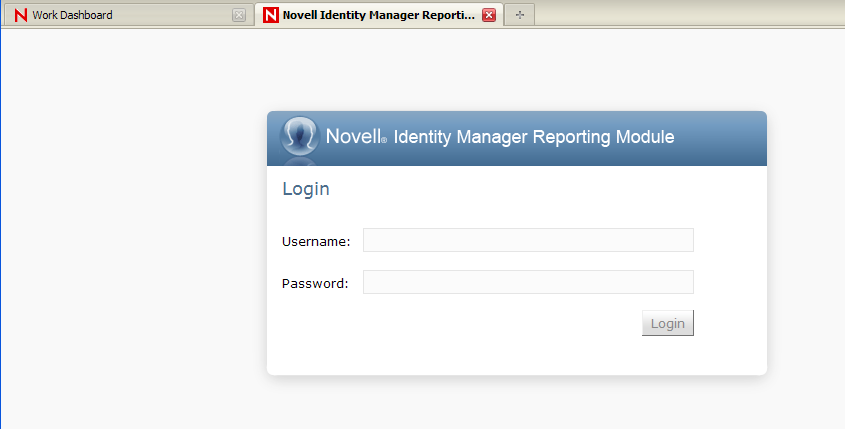
When Single Sign-On (SSO) is enabled for the Roles Based Provisioning Module, you do not see the Login page. Instead, you are logged into the reporting module automatically.
-
If SSO has not been enabled, log in as a Report Administrator or other user that has the navigation permission.
The reporting module displays the page:
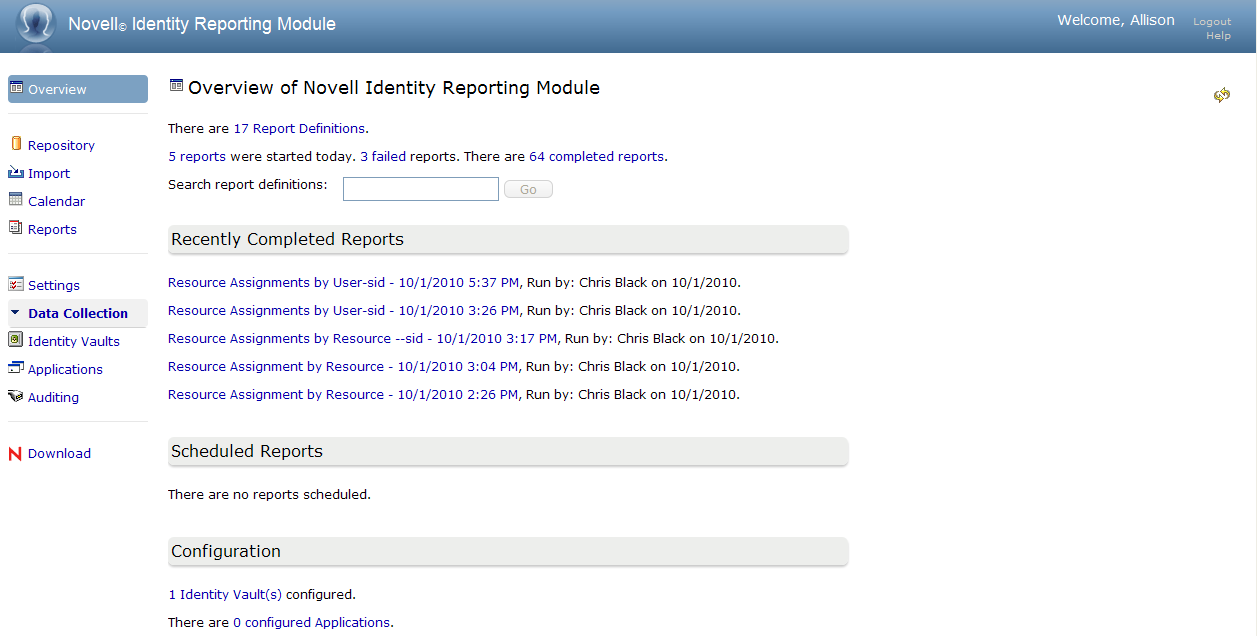
3.1.3 Configuring RBPM Access to the Reporting Module
To configure the Roles Based Provisioning Module so that it provides access to the Identity Reporting Module from the :
-
Configure the URL for the reporting module, as follows:
-
Log in to the RBPM User Application as a Configuration Administrator.
-
On the tab, navigate to .
-
On the page, specify the URL for the reporting module in the field. If the reporting module is running on the same server as the RBPM, you can use a relative URL such as /IDMRPT.
-
-
Optionally, enable SSO support:
-
Log in to the RBPM User Application as an Application Administrator.
-
On the tab, navigate to .
-
Select under .
-
On the page, select for .
-
NOTE:For SSO to work, cookies must be enabled on the client browser in which the user is running the User Application and the Identity Reporting Module. If cookies are disabled in the browser, the user sees the Login page when clicking on the button on the .
3.1.4 Configuring Reporting to Work with Novell Access Manager
If you want to integrate Novell Access Manager and the Identity Reporting Module, you need to be aware that Novell does not not currently support direct Single Sign On (SSO) between the two products. Instead, one must first access the User Application via Novell Access Manager, and then press the button on the left-hand navigation menu within the Work Dashboard.
To use this configuration, you need to perform some manual steps to configure the User Application and Novell Access Manager.
To configure the User Application:
-
Enable the setting:
-
Login to the User Application as the Administrator and go to .
-
Select the radio button next to .
-
Press the button.
-
Logout.
-
-
Correct the URL for the Identity Reporting Module:
-
Login to the User Application as the Administrator and go to .
-
In the text field to the right of ensure that the URL to the Reporting module is correct.
-
Press .
-
Logout.
-
To configure Novell Access Manager:
-
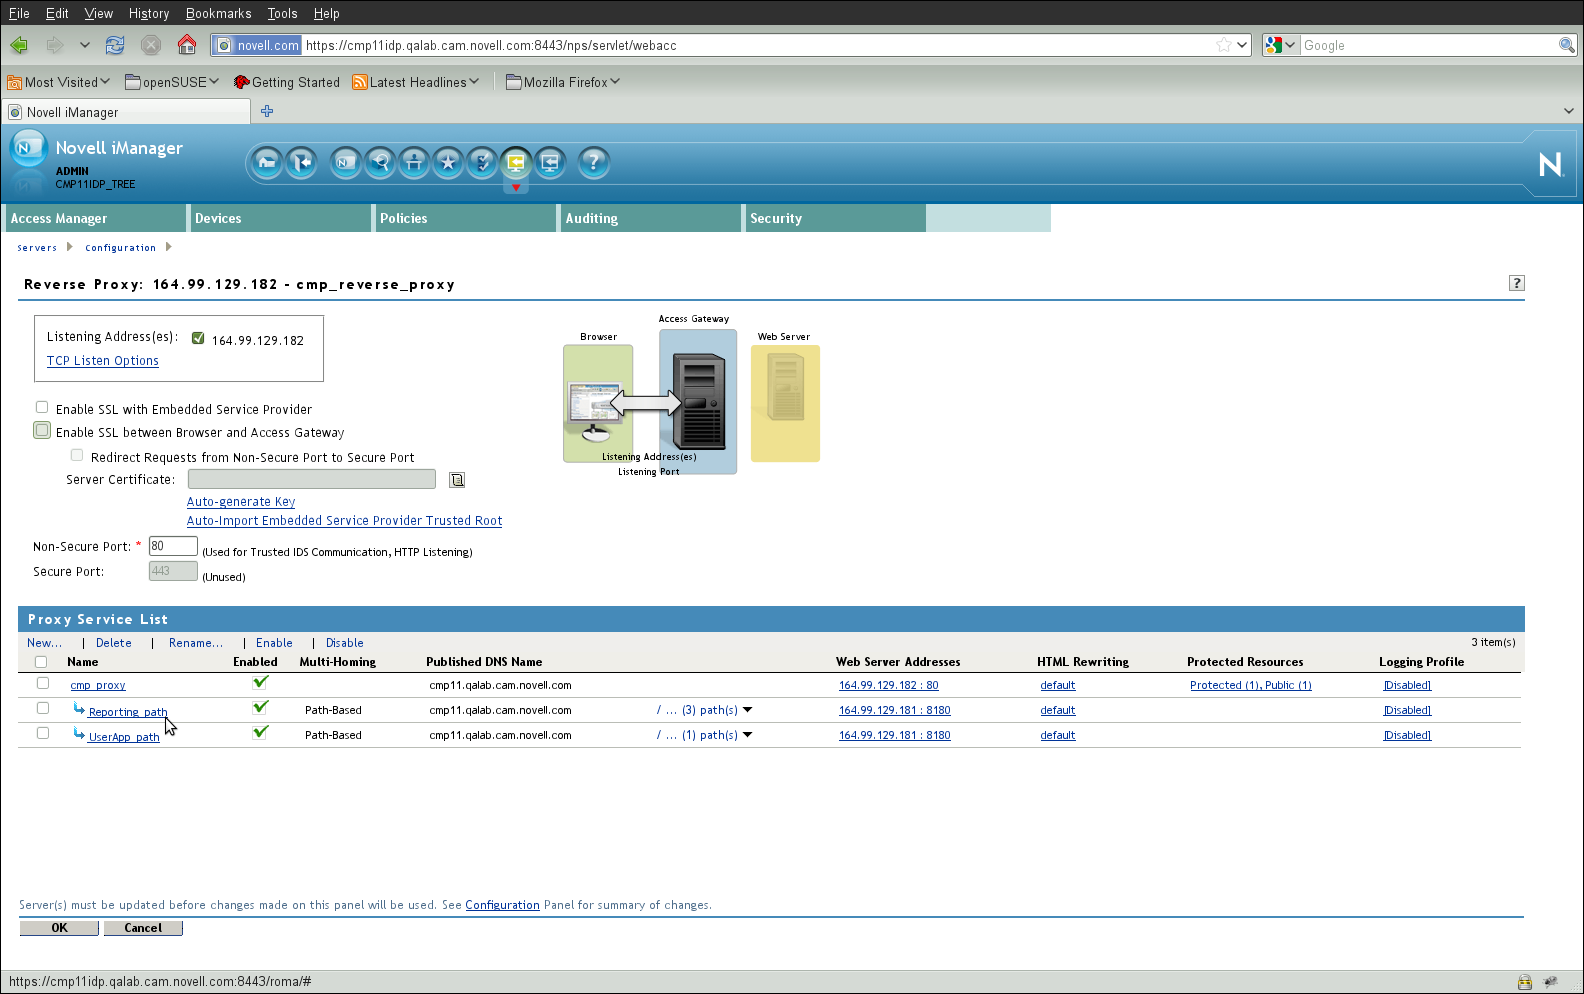
Create an entry for reporting in the .
-
You must add all three WAR files to the Path List:
-
/IDMRPT
-
/IDMRPT-AUTH
-
/IDMRPT-CORE
-
-
In the section add the follow entry:
ProxyErrorOverride on -401 -403
-
On the Tab, make sure that the entry is the actual DNS name of the machine that the reporting module is deployed on.
-
Configure the Protected Resource.
It is not necessary to create or enable Authorization, Identity Injection, or Form Fill for the Identity Reporting Module. You only need to configure the Protected Resource. You can apply the same entries you are using for the User Application, but keep in mind that the end user will not be signed on with SSO directly from Access Manager. The end user will still see the login for the Identity Reporting Module.
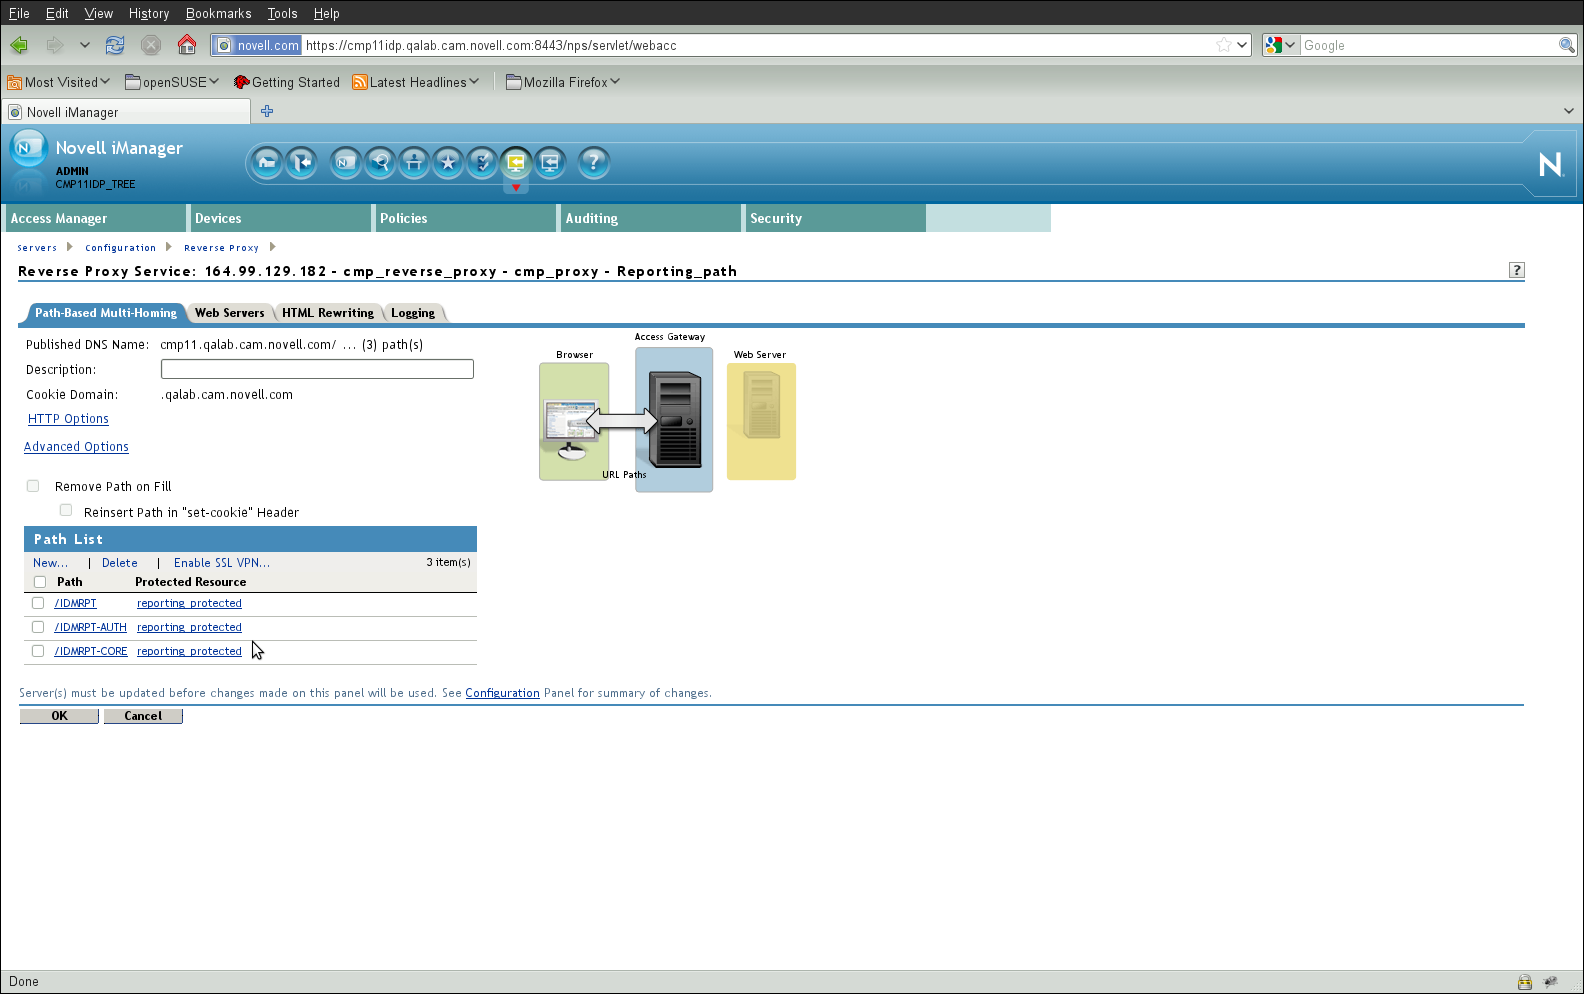
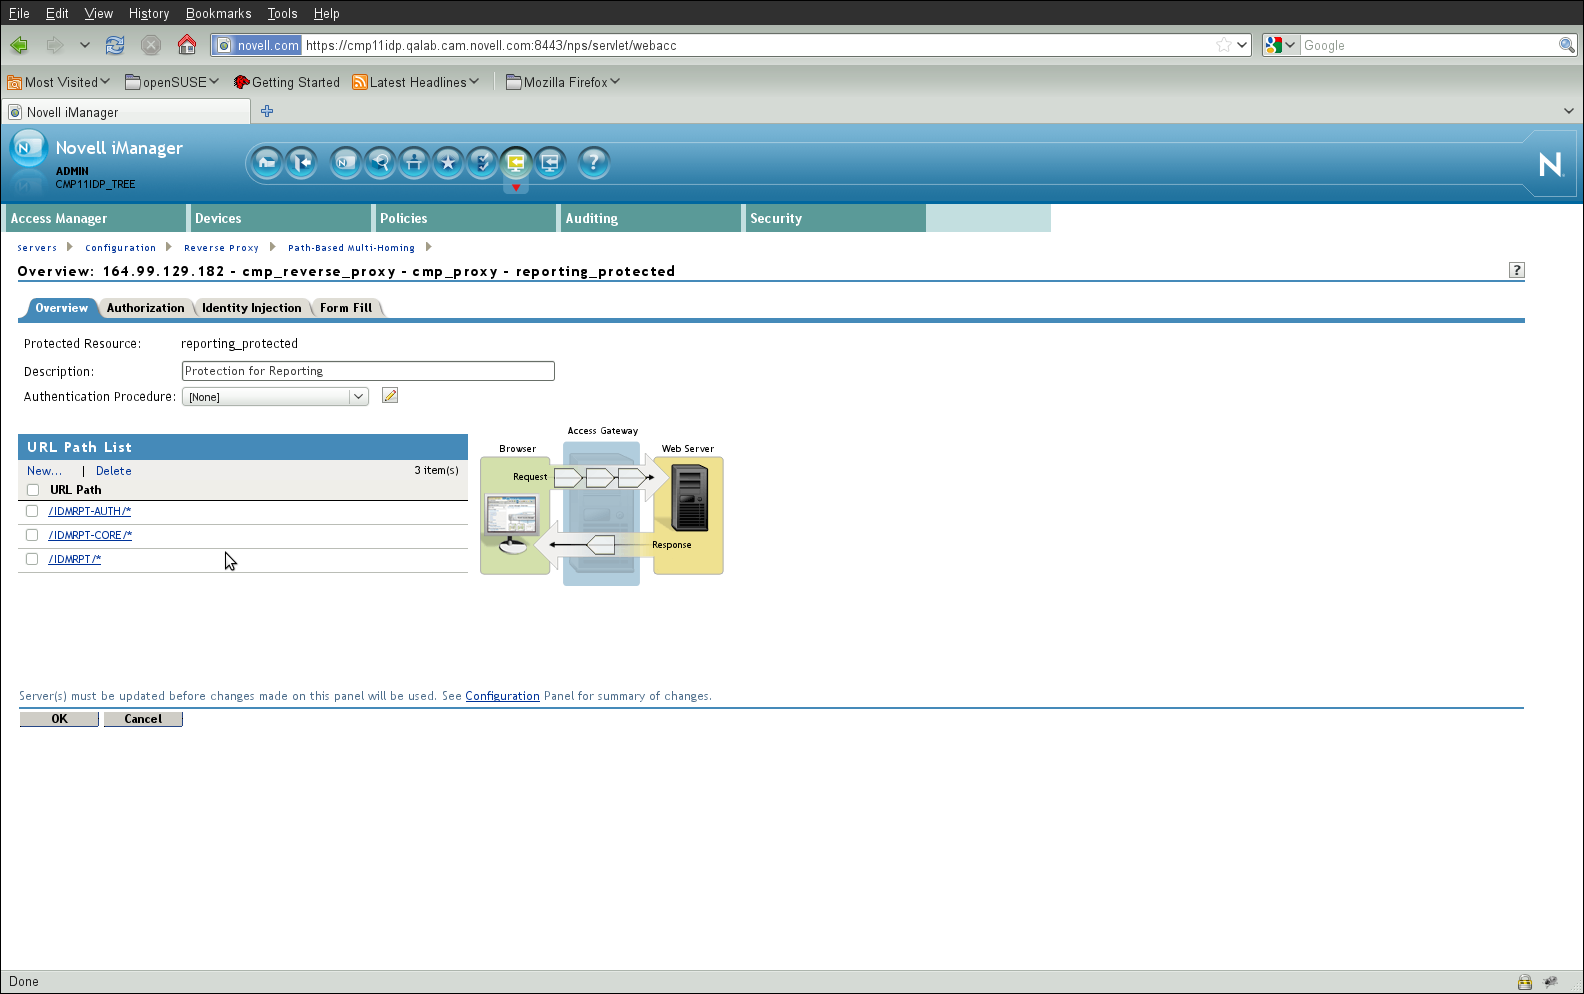
Once these manual steps have been performed, the Reporting Administrator can use the configuration.
To use the configuration:
-
Access the User Application via Access Manager, where you will be signed on with SSO.
-
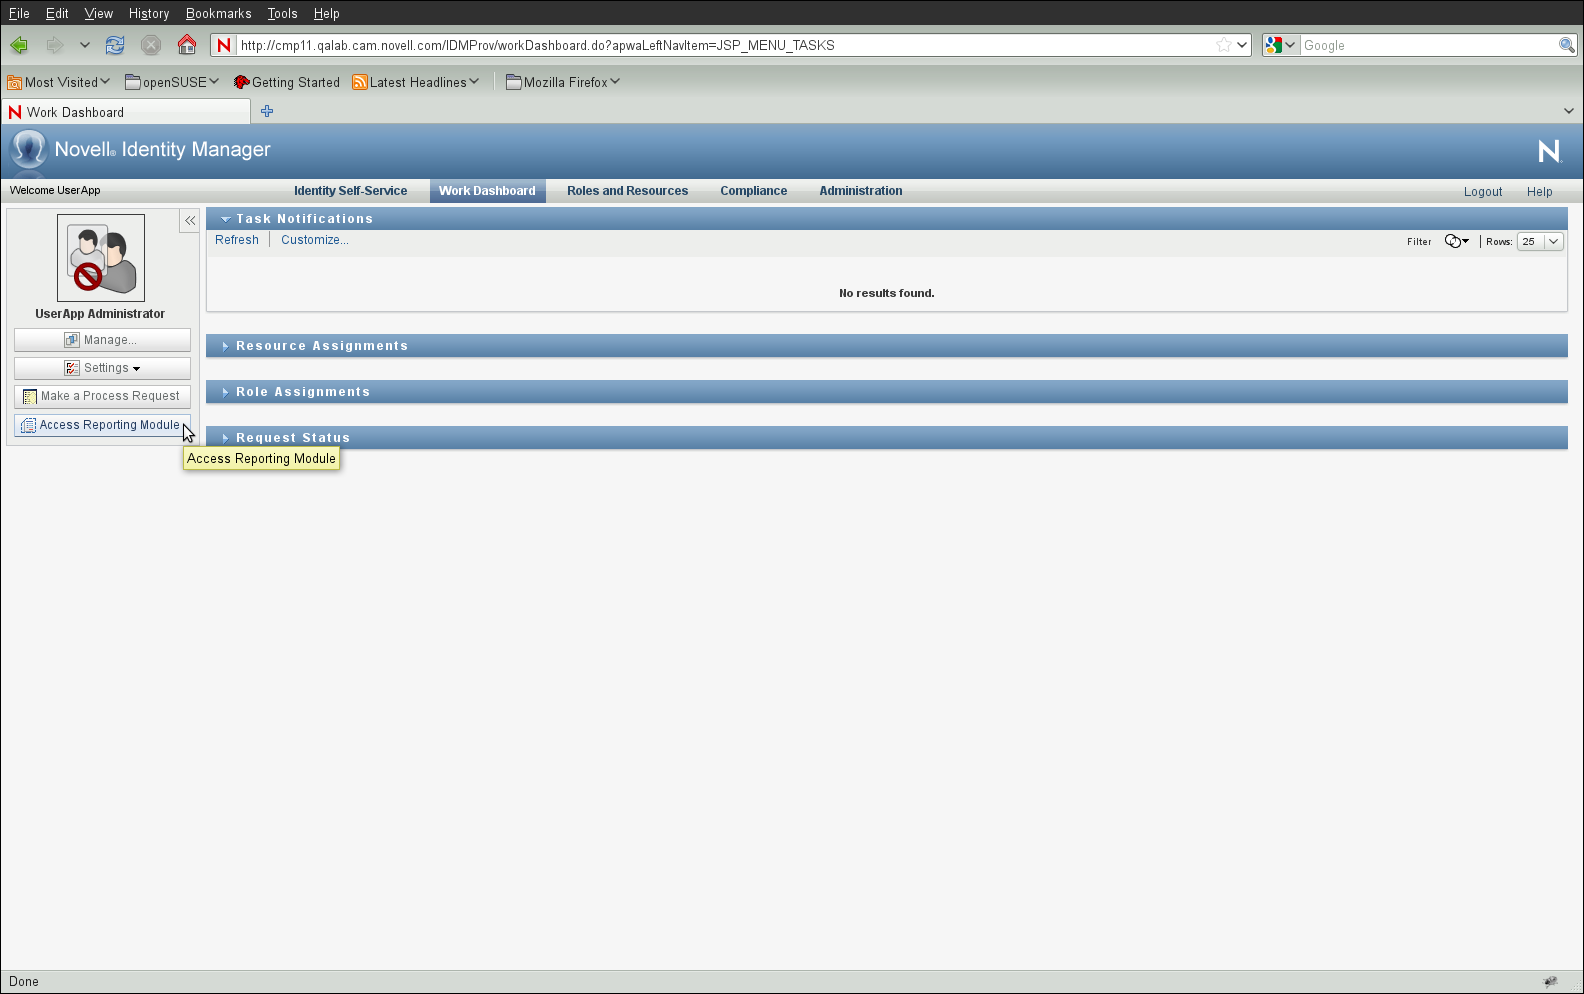
Press the button on the left-hand navigation menu on the Work Dashboard.
-
A new browser window will appear and the Reporting Administrator will be automatically logged into the Reporting Module. The URL in the browser will appear as the one controlled by Access Manager.