1.1 Ease of Management through OpenText Identity Console
OpenText eDirectory allows for easy, powerful, and flexible management of network resources. It also serves as a repository of user information for groupware and other applications. These applications access your directory through the industry-standard Lightweight Directory Access Protocol (LDAP).
OpenText eDirectory ease-of-management features include a powerful tree structure, an integrated management utility, and single login and authentication.
OpenText Identity Console lets you manage the directory and users, and access rights and network resources within the directory, from a Web browser and a variety of hand-held devices. The OpenText Identity Console gives you access to basic directory management tasks, and to the OpenText eDirectory management utilities you previously had to run on the OpenText eDirectory server, such as DSRepair, DSMerge, and Backup and Restore.
For more information, see the OpenText™ Identity Console Administration Guide.
1.1.1 Powerful Tree Structure
OpenText eDirectory organizes objects in a tree structure, beginning with the top Tree object, which bears the tree's name.
Whether your OpenText eDirectory servers are running Linux or Windows, all resources can be kept in the same tree. You won’t need to access a specific server or domain to create objects, grant rights, change passwords, or manage applications.
The hierarchical structure of the tree gives you great management flexibility and power. These benefits primarily result from the following two features:
Container Objects
Container objects allow you to manage other objects in sets, rather than individually. There are three common classes of container objects, as seen in Figure 1-2:
Figure 1-2 Common Classes of Container Objects
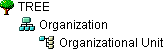
 The Tree object is the top container object in the tree. It usually contains your company’s Organization object.
 Organization is normally the first container class under the Tree object. The Organization object is typically named after your company. Small companies keep management simple by having all other objects directly under the Organization object.
 Organizational Unit objects can be created under the Organization to represent distinct geographical regions, network campuses, or individual departments. You can also create Organizational Units under other Organizational Units to further subdivide the tree.
Other classes of container objects are Country and Locality, which are typically used only in multinational networks.
 The Domain object can be created under the Tree object or under Organization, Organizational Unit, Country, and Locality objects.
You can perform one task on the container object that applies to all objects within the container. Suppose you want to give a user named Amy complete management control over all objects in the Accounting container, which contains the Database application, the Bookkeepers group, the LaserPrinter printer, and the users Amy, Bill, and Bob.
To do this, navigate to the Tree View on the home page of OpenText Identity Console and select the parent tree of the object in the left pane. In the right pane, select and then click > . Click and add Amy as a trustee. Next, click and select the rights you want Amy to have. Now Amy has rights to manage the Database application, the Bookkeepers group, the LaserPrinter printer, and the users Bill and Bob, in addition to herself.
Inheritance
Another powerful feature of OpenText eDirectory is rights inheritance. Inheritance means that rights flow down to all containers in the tree. This allows you to grant rights with very few rights assignments. For example, suppose you want to grant management rights to the objects shown in Figure 1-3.
Figure 1-3 Sample OpenText eDirectory Objects

You could make any of the following assignments:
-
If you grant a user rights to Allentown, the user can manage only objects in the Allentown container.
-
If you grant a user rights to East, the user can manage objects in the East, Allentown, and Yorktown containers.
-
If you grant a user rights to YourCo, the user can manage any objects in any of the containers shown.
For more information on assigning rights, see OpenText eDirectory Rights.