4.0 Provisioning Just-In-Time Access to AWS Services Using IAM Roles
Controlling granular privileged action on AWS through IAM roles by providing ephemeral account.
This is a sample scenario featuring Acme Corporation. This firm are in the process of migrating their applications and workload to SaaS platform name AWS.
This use case highlights the use of Privileged Access Manager in the following circumstances:
-
Delegated resource administration in vault
-
Secret level permissions in vault and ability to directly read secrets from Vault
-
Just in time (JIT) access with zero standing privileges
-
Support for AWS privilege access using ephemeral account
-
Support for PKI, where Privileged Access Manager acts as a Certificate issuer
This example refers to the following user profiles:
-
Fiona: An application administrator of Acme Corporation. Fiona needs occasional privileged access on AWS (managed by Steve) to perform application maintenance and configuration.
-
Adam: An administrator of Privileged Access Manager at Acme Corporation.
-
Aravanti: An application owner who manages and provides secure, on-demand access for application using secure access methods such as, PKI.
This section explains the prerequisites, flow of actions, and step-by-step configuration details to achieve this requirement.
Flow Diagram
The following diagram illustrates the sequential flow of configuration required for implementing the Just in time access framework:
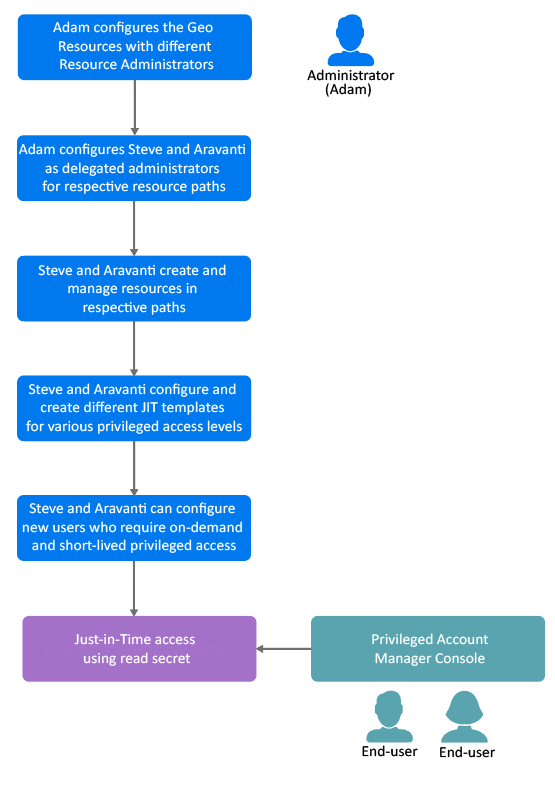
To achieve this requirement, Steve performs the following tasks:
After implementation of Just-in-Time access, the following are possible scenarios:
|
Scenario |
Result |
|---|---|
|
Administrator can log in and review. If required, can disconnect a session or revoke AWS secret for risky logins and audit logs. |
Each action is recorded, the live session video is captured, and stored in . No malicious activity can go undetected. |